GISEC Global 2027 Brings the Cybersecurity World Back to Expo City Dubai
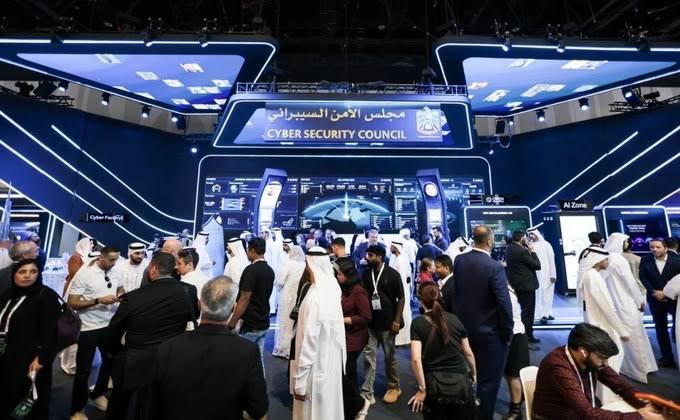
Cybersecurity leaders, government agencies, CISOs, ethical hackers, technology companies and startups will return to Dubai Exhibition Centre at Expo City from 4 to 6 May 2027 when GISEC Global stages its next major edition.
The event has developed into one of the world’s largest cybersecurity gatherings and the leading dedicated cyber platform across the Middle East and Africa.
Its scale reflects the growing importance of digital security.
Businesses are moving more operations online.
Governments are digitising public services.
Artificial intelligence is entering critical workflows.
Factories and infrastructure are becoming connected.
Cloud platforms hold enormous quantities of information.
And cybercriminals are becoming more sophisticated.
GISEC brings together the organisations defending this expanding digital environment.
The platform currently connects hundreds of global cybersecurity brands with tens of thousands of information-security professionals, government officials, security researchers and technology buyers from around the world.
For cybersecurity companies and professionals operating in Dubai, the event represents one of the most concentrated opportunities of the year to understand emerging threats, evaluate security technology and meet decision-makers responsible for protecting major organisations.
Cybersecurity Has Become a Boardroom Issue
Security was once treated largely as an IT responsibility.
That model no longer works.
A major cyber incident can interrupt an entire business.
Production can stop.
Customer data can be exposed.
Payments can fail.
Executives may face regulatory consequences.
Reputation can suffer.
Ransomware can lock organisations out of essential systems.
Cybersecurity therefore increasingly involves CEOs, boards, regulators and government leaders alongside technical teams.
GISEC reflects this broader responsibility by bringing senior decision-makers into the same environment as security engineers and researchers.
Ransomware Remains One of the Biggest Threats
Ransomware continues to affect organisations around the world.
Attackers enter networks, encrypt systems and demand payment.
Modern campaigns may also steal information before encryption.
Victims can therefore face two forms of pressure at once.
Restore operations or pay.
Prevent stolen data from being published or pay.
Defending against ransomware requires more than installing antivirus software.
Organisations need strong identity controls.
Network segmentation.
Protected backups.
Endpoint security.
Monitoring.
Incident-response plans.
Employee awareness.
No single product solves the problem.
This is one reason cybersecurity exhibitions increasingly showcase integrated security platforms rather than isolated tools.
AI Is Changing Both Attack and Defence
Artificial intelligence is accelerating another major change.
Defenders can use AI to analyse security alerts, identify suspicious behaviour and automate parts of incident investigation.
Security teams overwhelmed by thousands of alerts may benefit from systems capable of prioritising the most serious activity.
Attackers can use the same technology.
Phishing emails can become more convincing.
Messages can be personalised.
Malicious code can be modified.
Deepfake audio can imitate executives.
Synthetic video may support fraud.
The result is an increasingly automated competition between attackers and defenders.
GISEC 2027 will take place as organisations attempt to understand how much of this new security environment can safely be automated.
Identity Is Becoming the New Security Perimeter
Traditional cybersecurity often focused on protecting a corporate network.
Employees worked from offices.
Servers remained inside company buildings.
Firewalls separated trusted systems from the public internet.
Modern organisations operate differently.
Employees work remotely.
Applications run in the cloud.
Contractors connect from external devices.
Software-as-a-service platforms hold business information.
The old perimeter has weakened.
Identity has therefore become central.
Security teams need to understand who is accessing information, from which device and under what conditions.
Multi-factor authentication helps.
Privileged-access management matters.
Zero-trust strategies reduce automatic assumptions about who can be trusted.
Attackers know this.
Stolen usernames, passwords and session tokens are extremely valuable.
Zero Trust Is Moving From Slogan to Architecture
Zero trust is often summarised as “never trust, always verify.”
The practical implementation is more complicated.
Users should receive only the access they actually require.
Devices need evaluation.
Applications should be segmented.
High-risk activity may require additional authentication.
Access needs continuous review.
The objective is to reduce how far an attacker can move even after compromising one account.
For large organisations with thousands of employees and applications, this requires significant planning.
GISEC exhibitors increasingly provide identity, access, segmentation and monitoring technologies designed around these principles.
Cloud Security Continues to Expand
Cloud platforms have transformed how companies deploy technology.
Infrastructure can scale quickly.
Teams can launch services without purchasing physical servers.
But cloud adoption creates different security challenges.
One configuration error can expose sensitive information.
Access permissions can become extremely complicated.
Developers may create resources faster than security teams can monitor them.
Organisations increasingly use several cloud environments simultaneously.
Cloud-security platforms attempt to identify vulnerabilities, configuration problems and suspicious activity across these environments.
The difficulty is maintaining visibility as infrastructure changes constantly.
Application Security Is Moving Earlier
Companies release software faster than ever.
Development teams may deploy changes multiple times per day.
Security cannot wait until software is complete before testing begins.
This has encouraged approaches such as secure development lifecycles and DevSecOps.
Automated tools scan code.
Dependencies are checked for known vulnerabilities.
Secrets can be detected.
Applications can be tested continuously.
The principle is straightforward.
Finding a security problem before software reaches production is generally easier than responding after attackers discover it.
Web Applications Remain Attractive Targets
Public websites and applications are constantly exposed to the internet.
Attackers search for weaknesses.
Poor authentication.
Injection vulnerabilities.
Broken access control.
Server-side request forgery.
Insecure APIs.
Misconfigurations.
Modern applications also depend heavily on third-party packages and cloud services.
This increases complexity.
Security testing therefore needs to cover both custom code and the wider technology supply chain.
GISEC’s exhibitor ecosystem includes companies focused specifically on application and API protection.
Operational Technology Security Is Becoming Critical
Factories, energy companies, utilities and transportation systems depend on operational technology.
These systems control physical processes.
A compromise can therefore have consequences beyond stolen data.
Production can stop.
Equipment can be damaged.
Safety may be affected.
Historically, many industrial systems were isolated from normal business networks.
Digital transformation has connected more of them.
That brings efficiency but also creates cyber risk.
Security professionals increasingly need knowledge of both IT systems and industrial environments.
Critical Infrastructure Requires National Cooperation
Electricity.
Water.
Telecommunications.
Transport.
Healthcare.
Financial systems.
Modern societies depend on digital infrastructure supporting each of these sectors.
A serious attack can create national consequences.
Governments therefore treat cybersecurity as a strategic issue.
GISEC is supported by major UAE cybersecurity and security authorities and has developed a strong public-private collaboration model.
Government agencies can meet technology providers.
National security leaders can exchange information.
Private companies can understand emerging regulatory expectations.
This collaboration is particularly important because attackers do not respect organisational boundaries.
Security Operations Centres Are Becoming More Automated
Security Operations Centres, commonly known as SOCs, monitor systems for suspicious activity.
Analysts investigate alerts.
They examine logs.
They identify compromised accounts.
They respond to incidents.
The challenge is volume.
Large organisations generate enormous quantities of security information.
A team may receive thousands of alerts.
Many will not represent genuine attacks.
Security automation can help prioritise activity and collect investigation data.
But organisations need to avoid blindly automating decisions that require human judgement.
The future SOC will likely combine experienced analysts with increasingly powerful AI-assisted tools.
Threat Intelligence Helps Organisations Understand Adversaries
Not every organisation faces the same attackers.
A bank may be targeted for financial gain.
A government agency may face espionage.
Manufacturers can face intellectual-property theft.
Critical infrastructure may attract politically motivated attackers.
Threat intelligence helps organisations understand who may target them and how.
Indicators of compromise can be shared.
Attack techniques can be studied.
Security controls can then focus on realistic threats rather than theoretical possibilities.
Cybersecurity Startups Get a Global Platform
GISEC has developed one of the cybersecurity sector’s largest startup ecosystems.
Young companies can demonstrate new products to investors, customers and established technology businesses.
Cybersecurity is particularly attractive to startups because new problems constantly emerge.
Cloud adoption creates new needs.
AI creates new risks.
Identity systems evolve.
Quantum computing creates future cryptographic challenges.
Startups can move rapidly when larger vendors are slower to respond.
But the market is crowded.
Founders need to demonstrate that their technology solves a genuine security problem rather than simply adding another dashboard.
Investors Are Looking for Real Cybersecurity Businesses
Cybersecurity investment remains active because security spending is difficult for organisations to avoid.
But investors increasingly expect proof.
Are customers paying?
Does the product solve a serious problem?
Can the company retain clients?
How crowded is the market?
Can the technology scale internationally?
GISEC’s investor programmes connect founders with venture capital firms, corporate investors, angels and family offices.
For startups, access to customers can be as important as access to funding.
Hackers Are Part of the Defence Community
Ethical hacking plays an important role in cybersecurity.
Security researchers attempt to identify weaknesses before criminals exploit them.
Penetration testers simulate attacks.
Bug bounty programmes reward researchers for responsibly reporting vulnerabilities.
Capture-the-flag competitions allow professionals to develop practical skills.
GISEC’s Hack-O-Sphere activities bring this technical side of cybersecurity into the exhibition environment.
The message is important.
Understanding how attackers think is one of the best ways to build stronger defences.
Social Engineering Remains Extremely Effective
Not every attack requires sophisticated malware.
Sometimes the easiest way into an organisation is convincing someone to provide access.
A fake email appears to come from a manager.
A caller pretends to be technical support.
An employee is persuaded to approve an authentication request.
AI-generated voices may make impersonation more convincing.
Security awareness therefore remains essential.
Technology can block many attacks.
It cannot completely eliminate human decision-making.
Quantum Computing Creates a Future Security Problem
One of the biggest long-term cybersecurity issues involves quantum computing.
Current encryption protects banking, government communications, business information and internet traffic.
Future sufficiently capable quantum computers could potentially undermine some widely used cryptographic methods.
The danger is not limited to the future.
Attackers can steal encrypted information today and potentially attempt to decrypt it years later.
Organisations therefore need to begin understanding post-quantum cryptography before large-scale quantum computers arrive.
This is why GISEC Global 2027 will be joined by the new Global Quantum X event.
Security Is Becoming a Continuous Process
Companies sometimes treat cybersecurity as a project.
Install software.
Complete an audit.
Pass compliance.
Move on.
Real security does not work like that.
Systems change.
Employees join and leave.
New vulnerabilities appear.
Attackers change tactics.
Cloud environments expand.
Acquisitions introduce new networks.
Cybersecurity therefore requires continuous monitoring and improvement.
GISEC provides a yearly snapshot of how quickly those challenges are evolving.
Three Days at the Centre of the Cybersecurity Economy
From 4 to 6 May 2027, Dubai Exhibition Centre will again become a meeting point for the people defending the digital economy.
CISOs will evaluate security platforms.
Government leaders will discuss national resilience.
SOC analysts will study new detection tools.
Ethical hackers will test their skills.
Startups will meet investors.
Technology companies will compete for enterprise customers.
And organisations will confront the uncomfortable reality that cyber risk cannot be eliminated completely.
The objective is stronger resilience.
Prevent as much as possible.
Detect what gets through.
Respond quickly.
Recover effectively.
GISEC Global 2027 provides three days for the international cybersecurity community to work on every part of that challenge.